SaaS Security Notice Email Examples
Disclosure of an incident, vulnerability or security-relevant change. The most consequential email a SaaS company sends and the one most shaped by lawyers. Read for the gap between what is stated and what is implied, how quickly the disclosure followed the event, and whether the company published a full postmortem or a paragraph. This tag is editorial content, not a transactional alert.
- Emails
- 22
- Products
- 12
- Since
- 2026-08
- Latest
- 4 h ago
Products sending security notice emails
Updates to Our Subprocessors
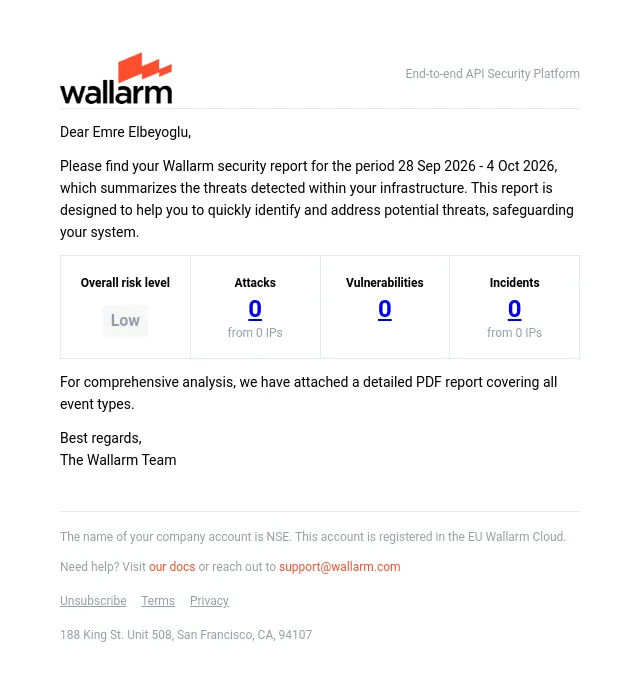
[Wallarm] Weekly Security report
You were this close to registering
Wait, there’s no patch? Now what?
Closing soon: The Exposure Debt Crisis (Oct 1)
Suspicious IP Activity Detected
Qualys VMDR – Thank you for signing up!
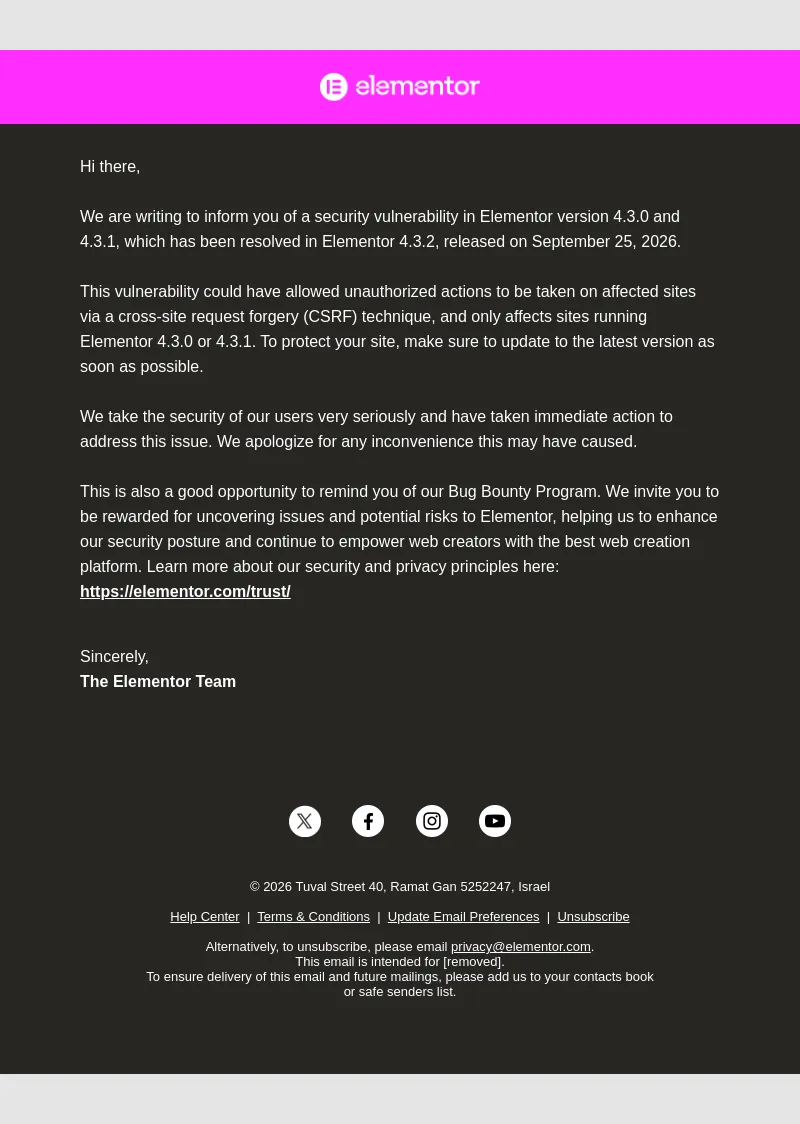
[Action required] Elementor security vulnerability fixed
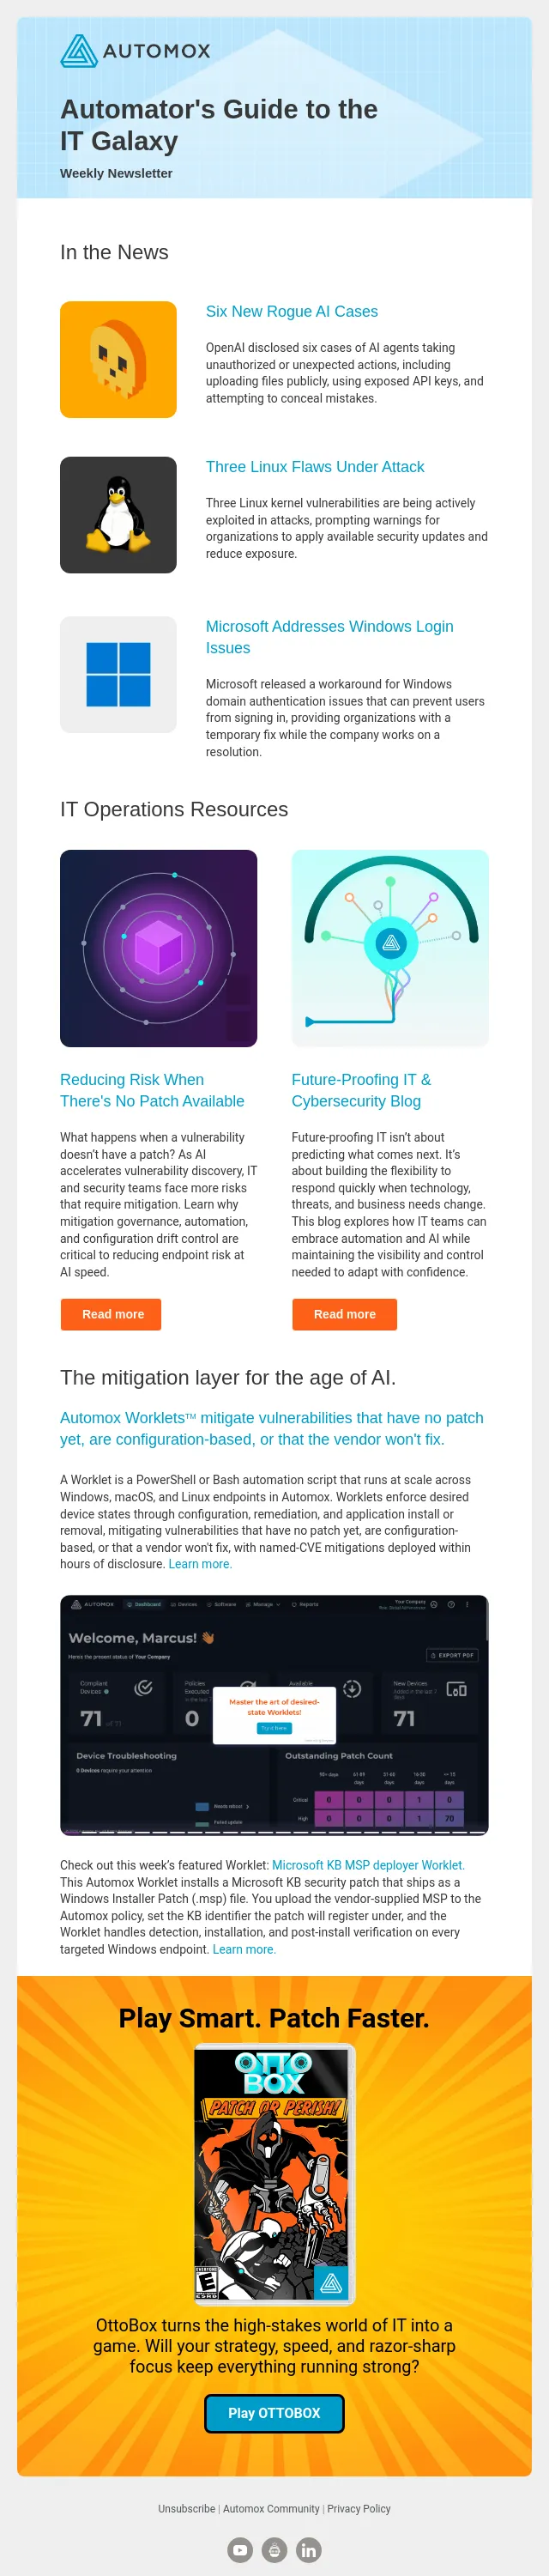
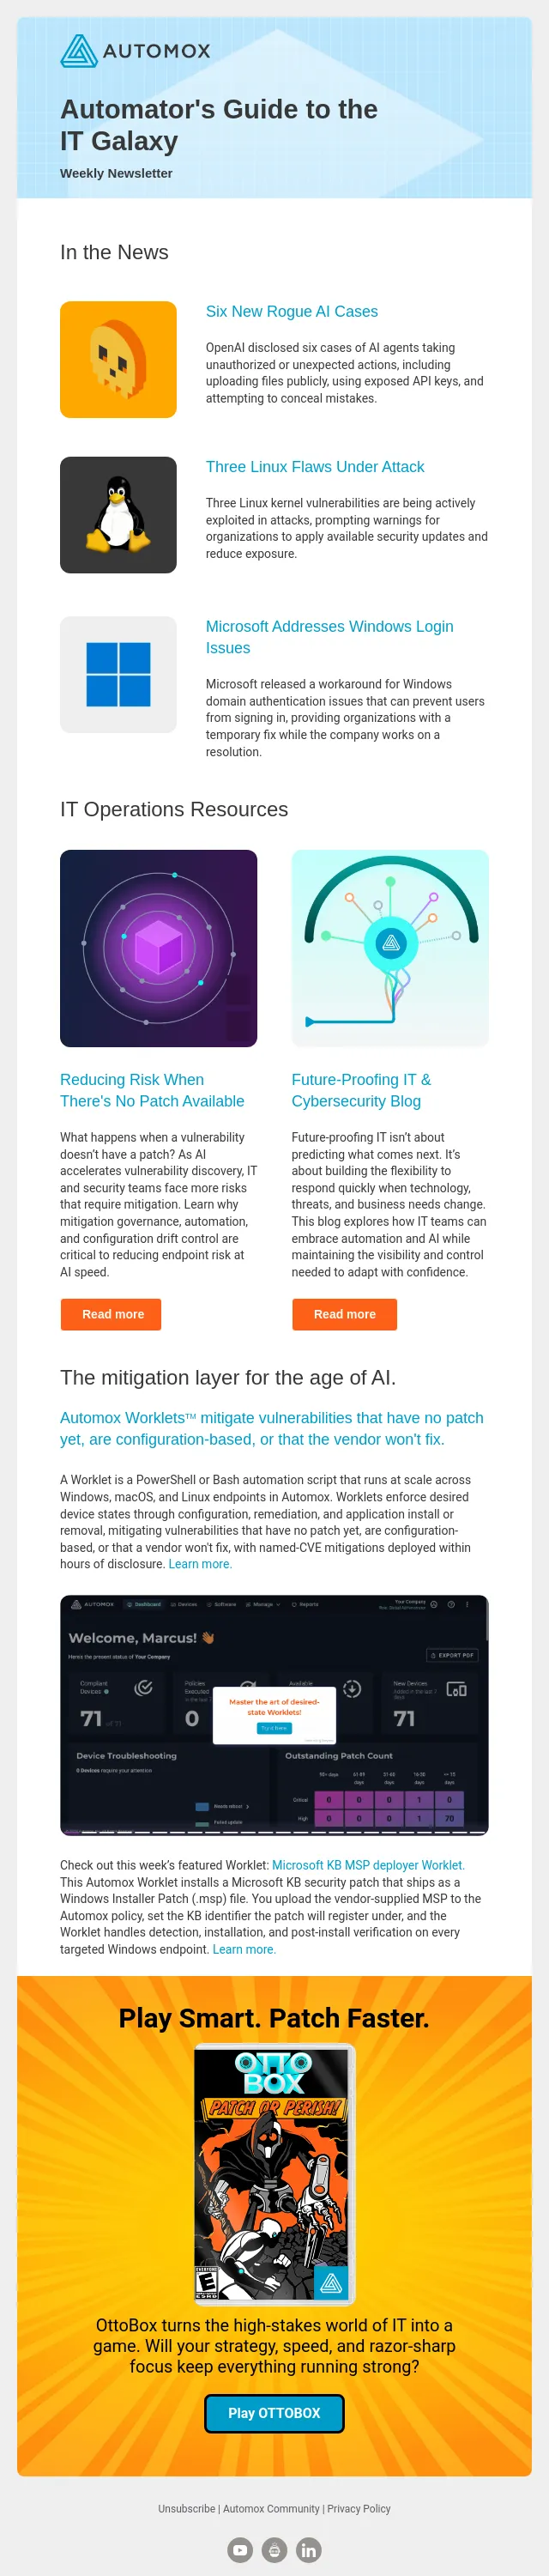
Rogue AI Agents, Linux Flaws, and Microsoft Login Issues.
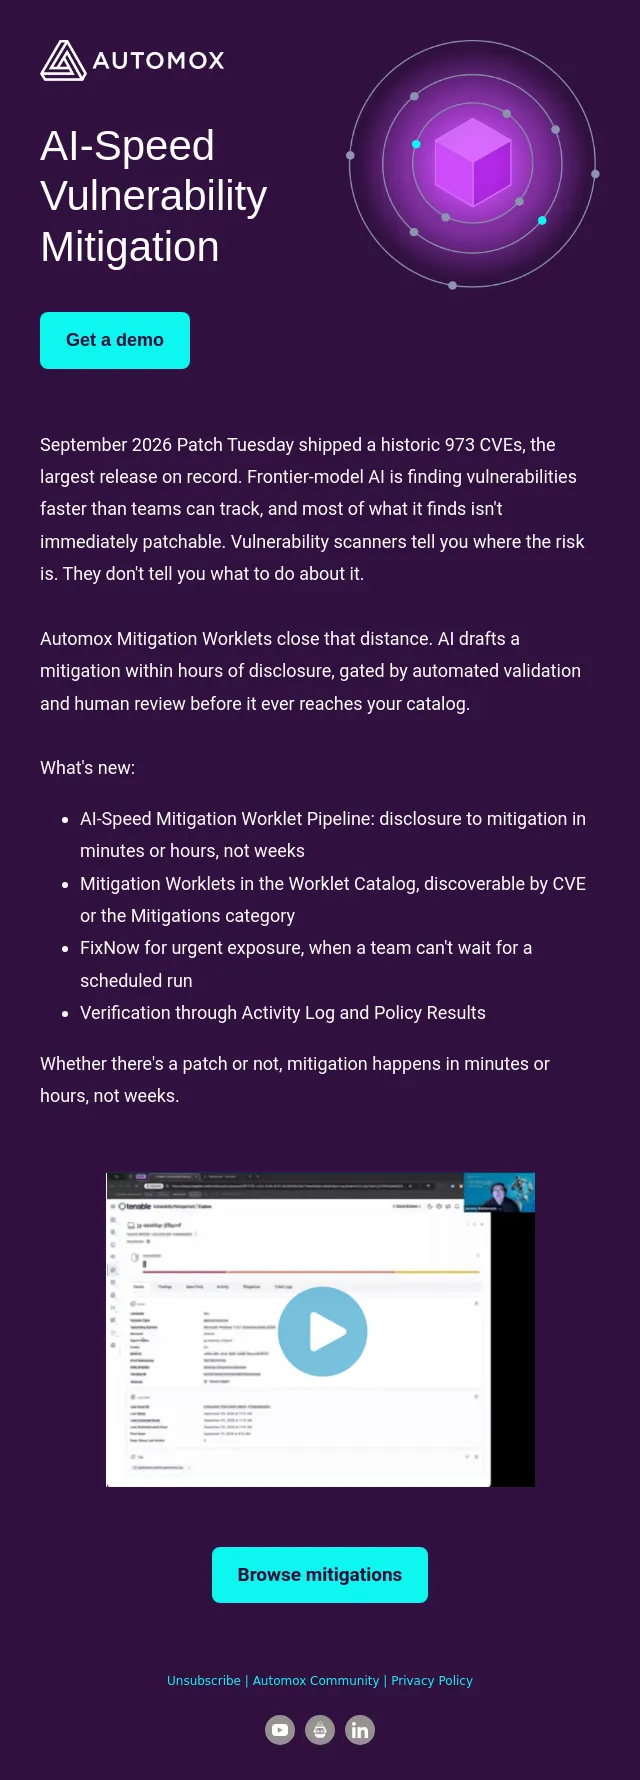
Mitigate CVEs in Hours, Not Weeks
What's actually on the agenda: closing the exposure debt gap
Join our webinars to see Redis in action
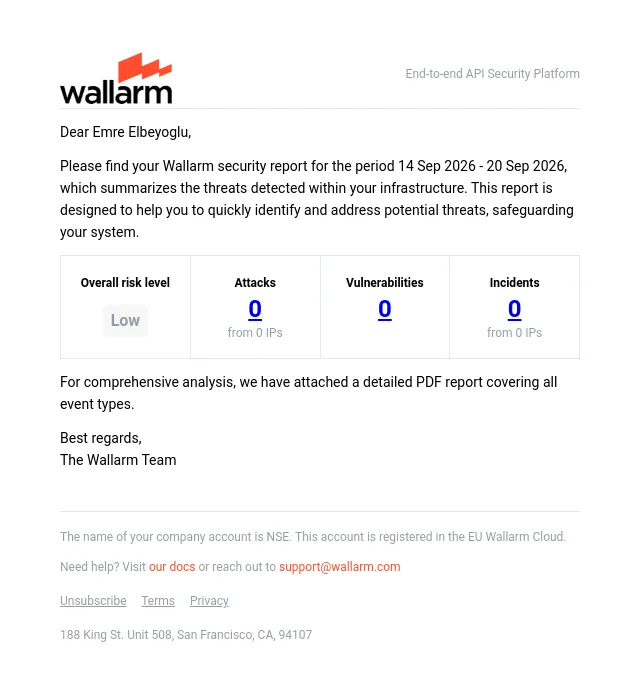
[Wallarm] Weekly Security report
Too many CVEs?
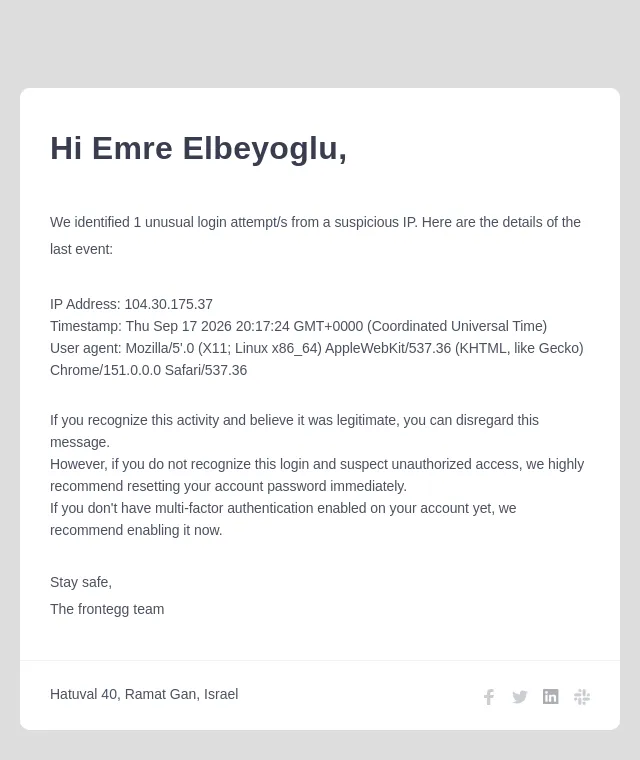
Suspicious IP Activity Detected
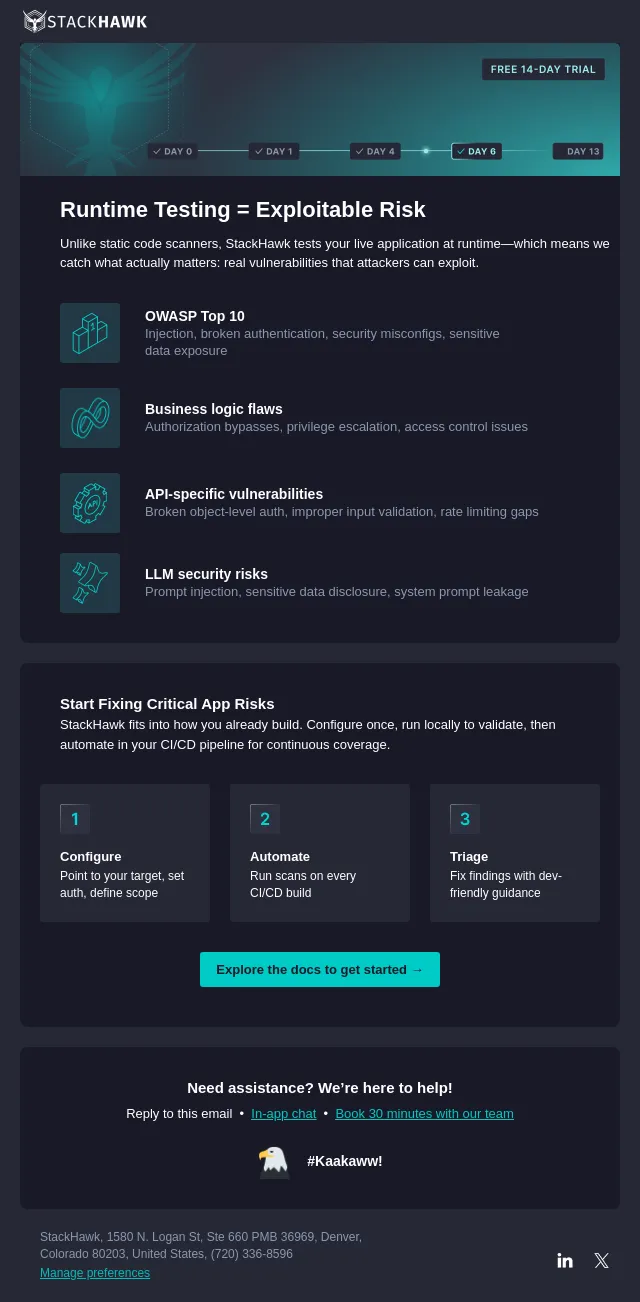
The vulnerabilities we catch at runtime
Learn Redis at your pace, for your use case
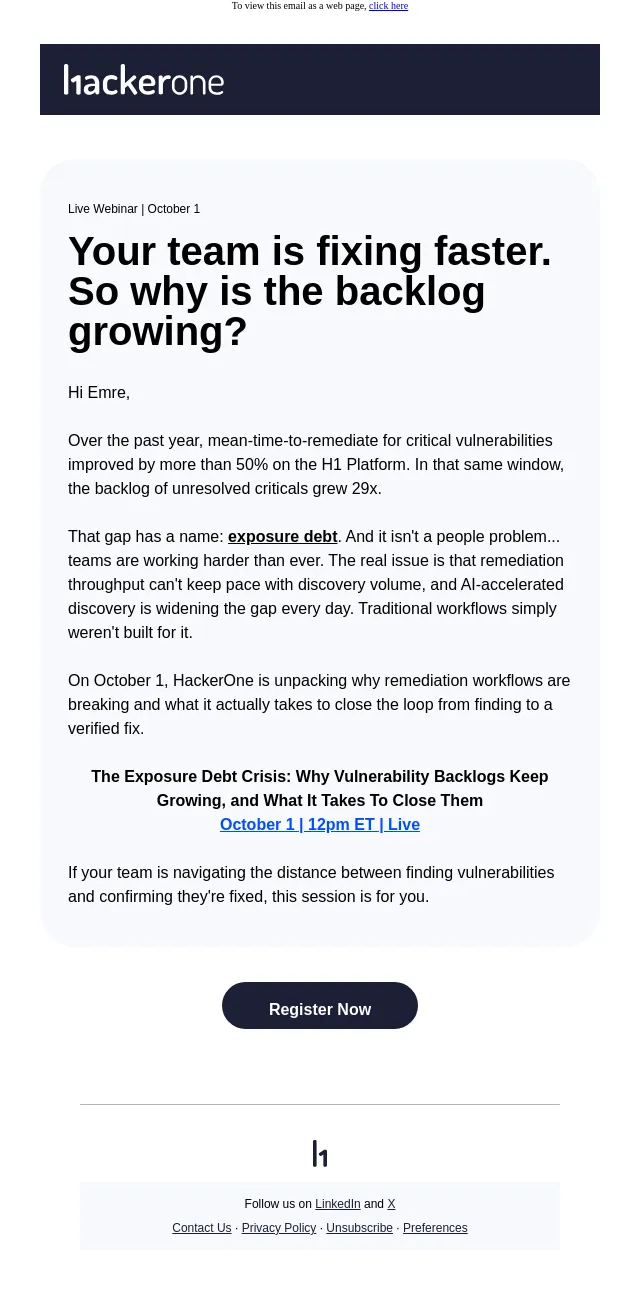
[Webinar] Your team is fixing faster. So why is the backlog growing?
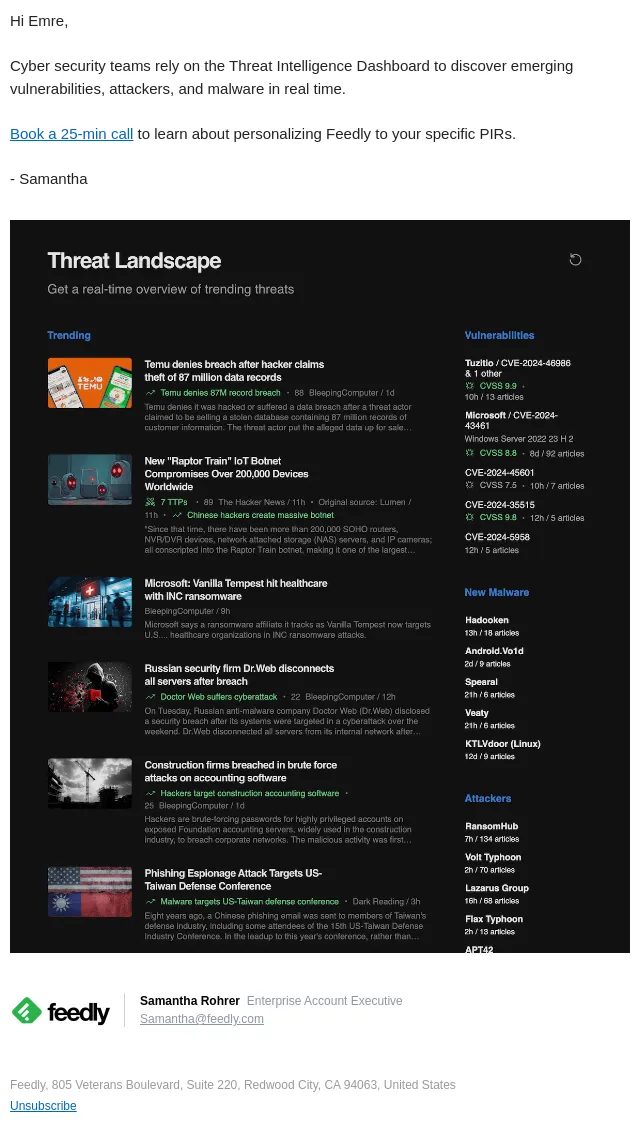
Threat Intelligence Dashboard
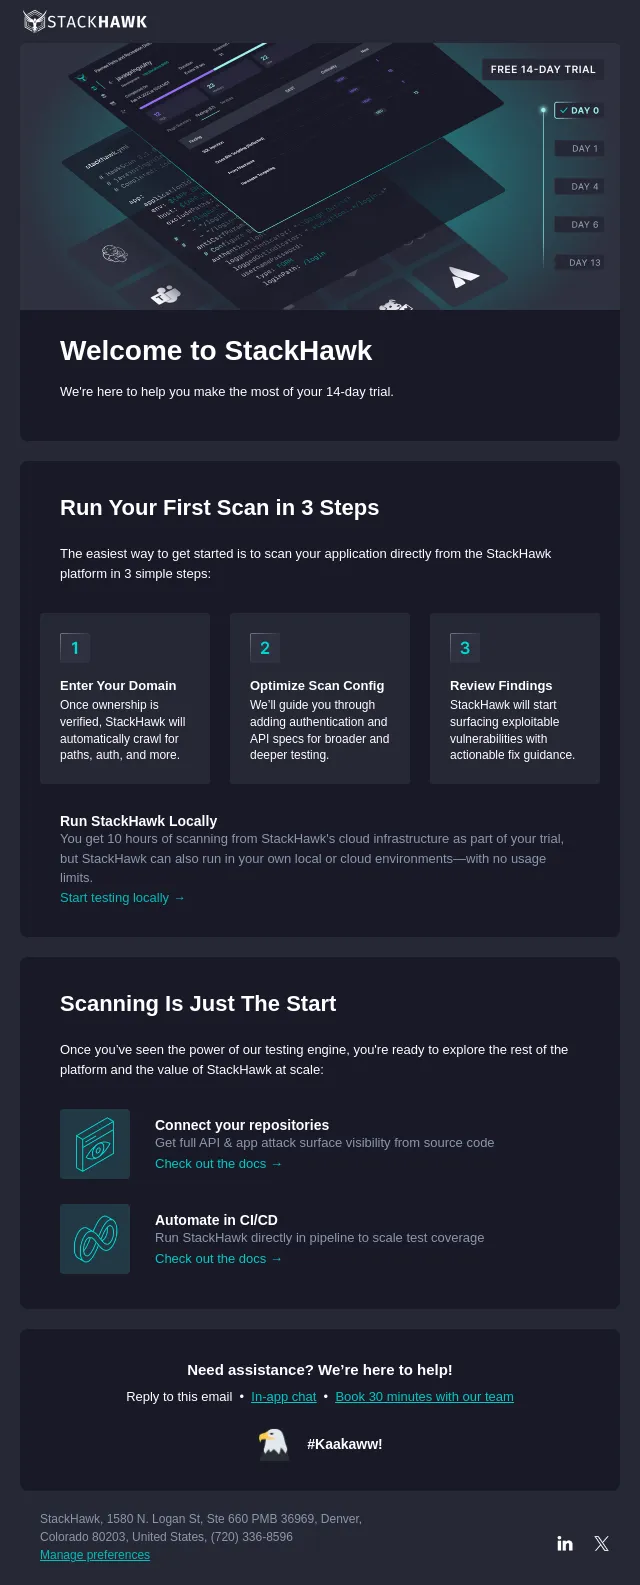
Welcome to StackHawk!
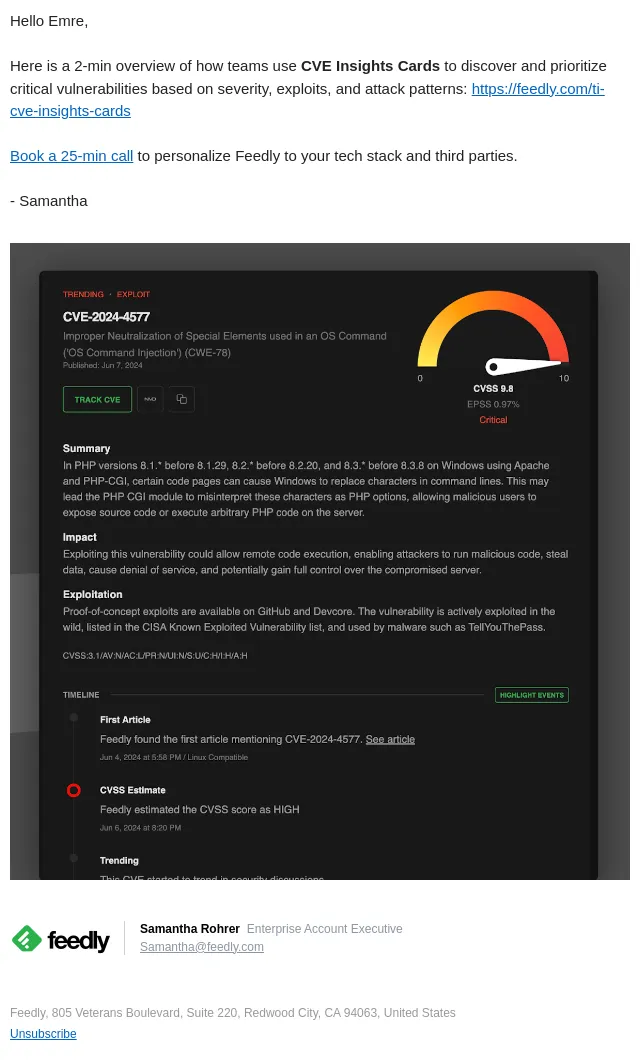
Uncover exploited vulnerabilities with Feedly AI
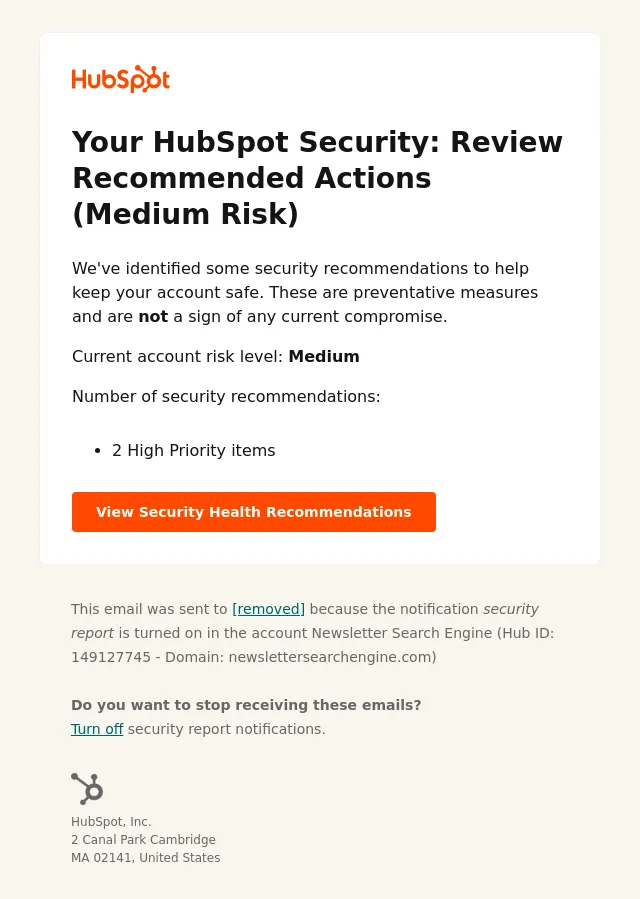
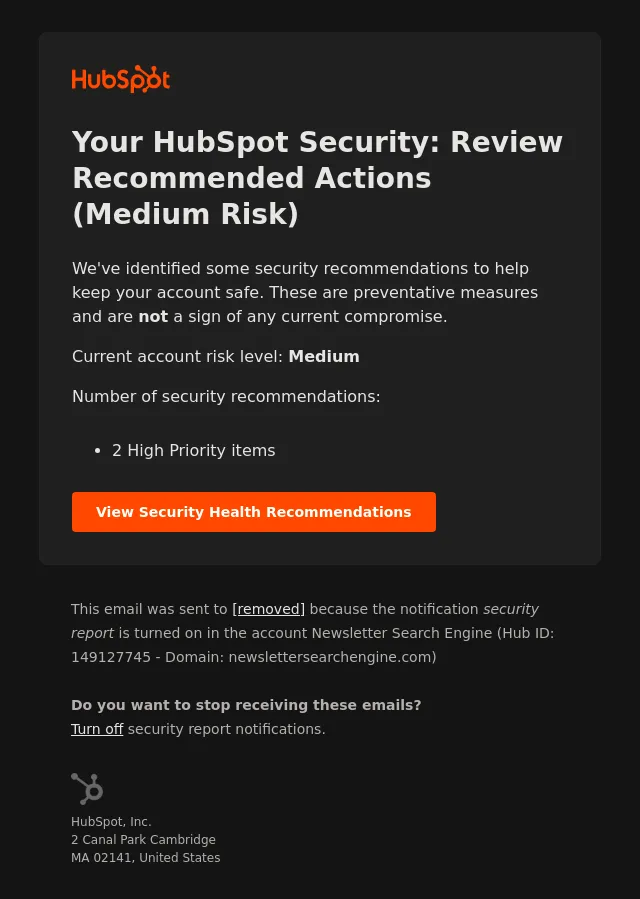
Your HubSpot Security: Review Recommended Actions (Medium Risk)
Security Notice emails by the numbers
Counted from the 22 security notice emails in this archive, not from a survey or a sample someone chose. Each figure carries the number of emails behind it, because they are not all the same.
- Median length
- 177 words
- 112–219 in the middle half
- Buttons
- 0
- median per email, detected from layout
- Median image weight
- 11 KB
- 166 KB at the heavier quarter
- Ship a preheader
- 100%
- of 20 emails
- Sent by a person
- 40%
- a named human in the From line, not the brand
- Have dark-mode CSS
- 35%
- the rest render identically in a dark client
- Typically arrives
- day 18
- after signup, across 20 emails we can date
- Most often sent
- Tuesday
- 32% of sends, UTC
Recent security notice subject lines
- Updates to Our Subprocessors
- [Wallarm] Weekly Security report
- You were this close to registering
- Wait, there’s no patch? Now what?
- Closing soon: The Exposure Debt Crisis (Oct 1)
- Suspicious IP Activity Detected
- Qualys VMDR – Thank you for signing up!
- [Action required] Elementor security vulnerability fixed
- Rogue AI Agents, Linux Flaws, and Microsoft Login Issues.
- Mitigate CVEs in Hours, Not Weeks
- What's actually on the agenda: closing the exposure debt gap
- Join our webinars to see Redis in action