What's new at Speakeasy: Private MCP Gateway on Tailscale, Shadow AI Detection and Role-Based Plugins
Take your MCP gateway off the public internet, see every AI tool on company devices, and meet us at AGNTCon + MCPCon this week.
- Product
- Speakeasy
- Sent from
- speakeasy.com
- Sent
No dark-mode styles — this email renders the same in a dark client.
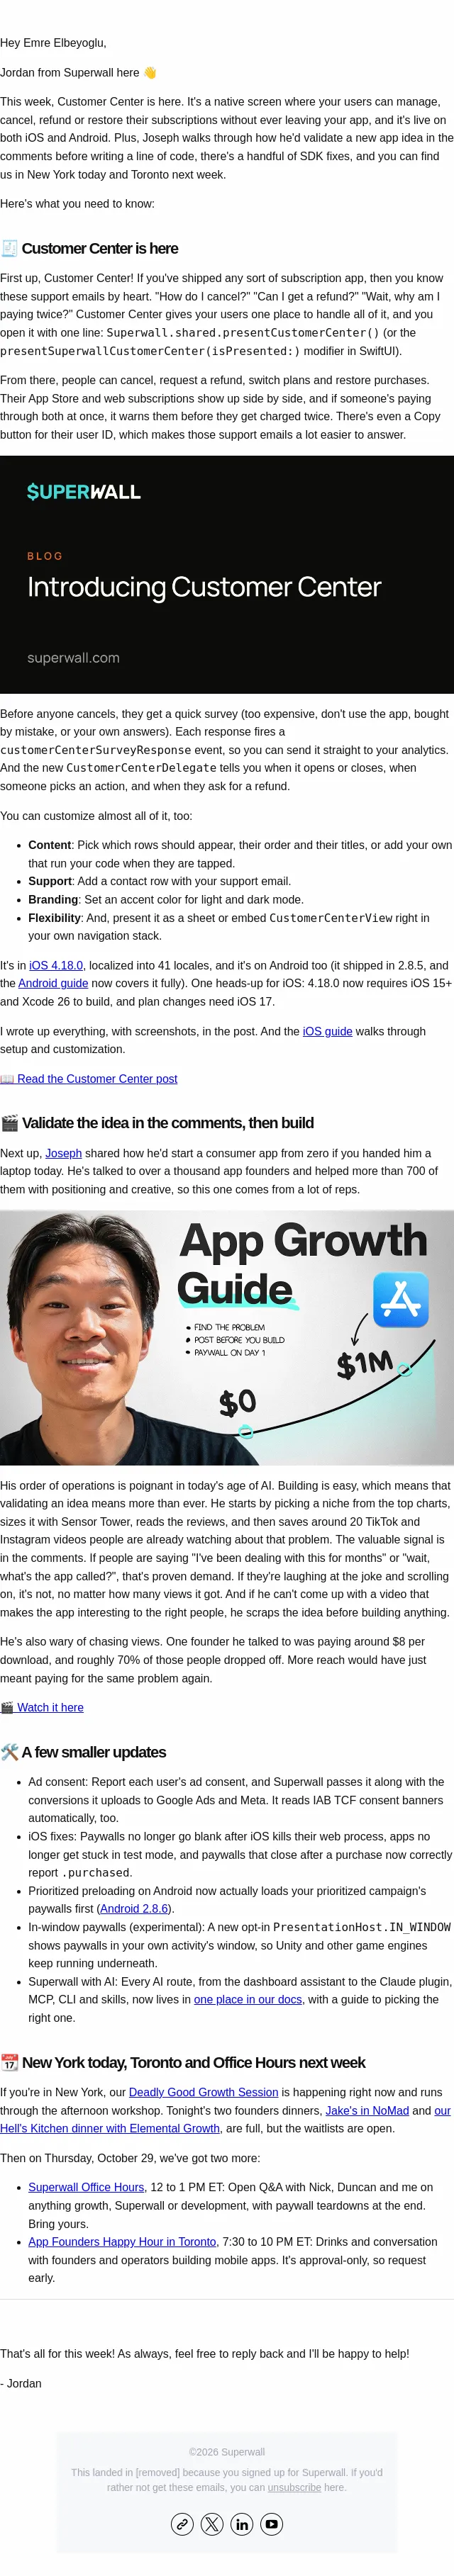
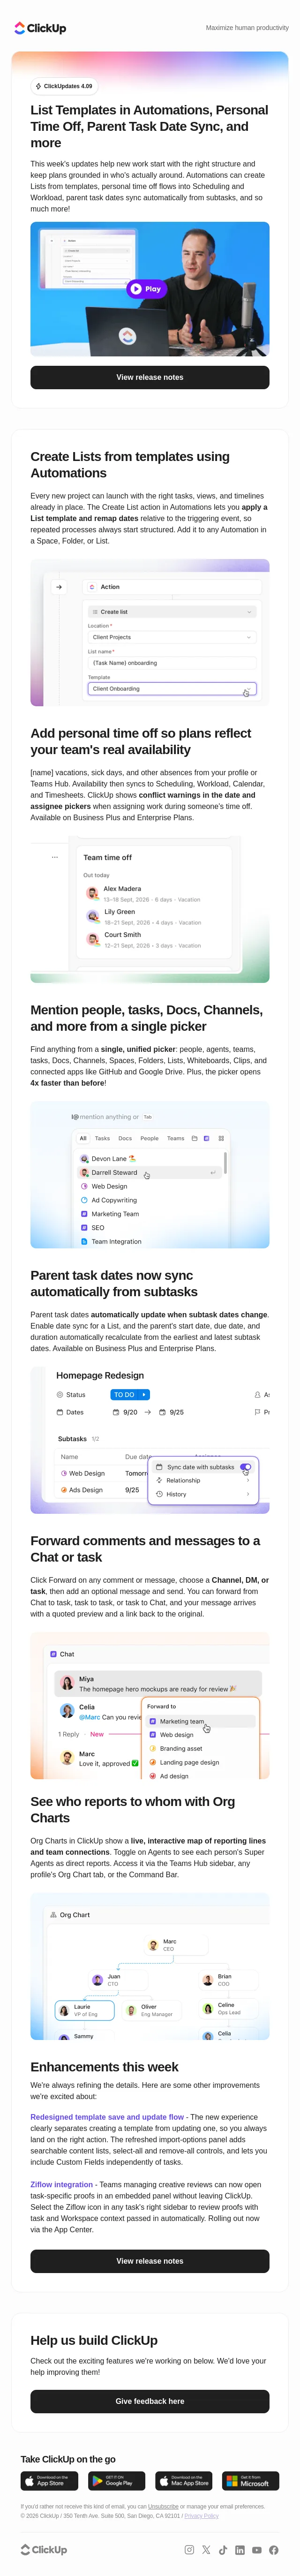
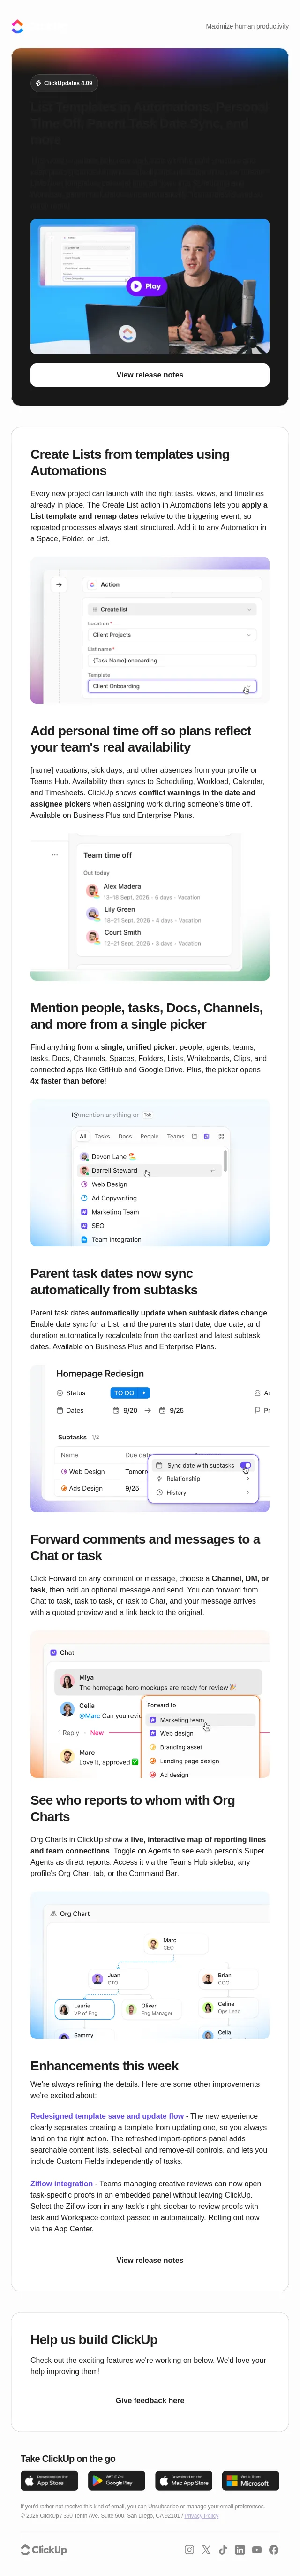
Take your MCP gateway off the public internet, see every AI tool on company devices, and meet us at AGNTCon + MCPCon this week. ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ ͏ OCTOBER 21, 2026 What's new? Rolling out AI across a company raises three questions that never go away: who can reach your tools, what's actually running on people's machines, how do we get the right tools get to the right teams. This month's releases answer each one. The MCP gateway can now run privately on your Tailscale tailnet. The device agent finds every harness, model, MCP server, and skill on enrolled laptops so you can approve or block them. And granting a role access to an MCP server now puts it straight into that role's plugin PRODUCT Private MCP gateway on Tailscale Your MCP servers, reachable only from your tailnete Until now, the MCP gateway lived on the public internet. An IP allowlist could filter who got in, but the listener was still public, and an IP address doesn't tell you much about who's actually calling. Speakeasy can now run the MCP gateway directly on your Tailscale tailnet, at a stable private hostname: * No public listener: set a server to private-only and every public route returns a 403. It fails closed, so a Tailscale outage never reopens the public path * Identity on every request: each call carries the Tailscale user, device, and tags, logged in your audit trail next to the tool that was called * Your tailnet ACLs govern access: no second allowlist to keep in sync, no stable egress IPs required, and IPv6 just works Each MCP server picks its own exposure (public-only, dual, or private-only), so you can migrate one server at a time. Rolling out per organization now. Reach out to have it enabled for yours. Read more [https://www.speakeasy.com/blog/release-private-mcp-gateway-tailscale] PRODUCT Shadow AI detection Every harness, model, MCP server, and skill on your company's devices Ask a security team what AI the company uses and you'll get the list that went through procurement. The real list is longer: a CLI agent someone tried over the weekend, Ollama left running on a laptop, a skill installed from a public repo. The Speakeasy device agent now finds that AI on enrolled devices and reports it to a single Shadow AI page: * Four kinds of shadow AI: harnesses like Claude Code, Codex, and Cursor, locally run models, MCP servers, and skills * Who uses what: each tool shows the people and devices using it, and when it was last seen * Approve or block: mark a harness Approved or Blocked with a rationale for the audit log, and the MCP gateway enforces the block at sign-in Matching happens on the device against a library of around 40 built-in scan targets, plus any custom targets you add. The agent never reads prompts, shell history, or usage data. Available now for organizations running the device agent (in beta), with scanning on macOS today. Read more [https://www.speakeasy.com/blog/release-shadow-ai-monitoring] PRODUCT Role-based plugins Grant a role access and its MCP servers show up automatically Getting MCP servers to a team used to take two steps: grant the role access, then edit the plugin people install in their AI client. Now every role has its own plugin, and the relevant servers get automatically distributed. No additional action needed. * Granting access adds the server: give a role access on the Team Access tab and Speakeasy adds the server to the role's plugin and publishes the update * Removing access removes it: unless another role on the same plugin still has access * Admins stay in control: curate plugins by hand at any time. Distribution never widens access, because the gateway still checks Team Access on every call * Universal plugin management: Every users is able to easily toggle their assigned plugins via the Speakeasy device agent. That enables plugin management across every agent they use. On for every organization today, with nothing to enable. Read more [https://www.speakeasy.com/blog/release-role-based-plugins] EVENT Meet us at AGNTCon + MCPCon October 22-23, San Jose McEnery Convention Center We're sponsoring AGNTCon + MCPCon North America this week, the Linux Foundation's conference for people building agents and MCP (formerly MCP Dev Summit). Two days, 150+ talks across 11 tracks, and 3,500+ attendees. If you're there, come find the Speakeasy team. We'd love to show you the private gateway and shadow AI detection in person. See the event [https://events.linuxfoundation.org/agntcon-mcpcon-north-america/] Book a demo [https://www.speakeasy.com/book-demo] Stay tuned for more updates from the team. We're excited to continue building and improving Speakeasy with your support and feedback. If you'd like to learn more about Speakeasy, please reach out [https://www.speakeasy.com/book-demo]. https://x.com/speakeasydev https://join.slack.com/t/speakeasy-dev/shared_invite/zt-1cwb3flxz-lS5SyZxAsF_3NOq5xc8Cjw https://www.linkedin.com/company/speakeasyapi/ You are receiving this email because you opted in to receive updates from Speakeasy Speakeasy, 90 New Montgomery St, Suite 700, San Francisco CA 94105 Unsubscribe [https://app.loops.so/unsubscribe/cmvh2zawm06yy01x30m0x8zcc/6a0877b18a3c9f17e88afede074581887063a2f0bed7dec7c670ccfe12652f81869a7ea5927e15ad87328f9df6975fa6a373afa56e63dae46735787f]
- Accession
- nse/speakeasy/2026-10-20/4597
- From
- Speakeasy · sagar@speakeasy.com
- Sent
- 20 October 2026 · 19:00 UTC